

What is access control in AI systems? It is the set of rules that determines who can use models, data, toolsand outputs. In practice, it answers a few straightforward questions: who is making the request, what are they allowed to accessand what are they allowed to do with the result?
That matters because not every employee, contractor, service accountor automated workflow should have the same level of access.A support agent may be allowed to use an assistant to summarize a customer ticket, while a payroll administrator may need access to a separate tool that works with compensation data.Treating both users the same creates needless risk.
Start With Identity and Clear Roles
Good access control begins with reliable identity management. Each person and service account should be uniquely identified,verified,and connected to an active business need. Shared logins and vague permissions make it harder to tell who used a system,what they accessed,and whether that access was appropriate.
Permissions should follow real responsibilities rather than informal exceptions. A simple role structure can definitely help:
- Viewer: can see approved AI outputs and shared knowledge.
- Contributor: can provide permitted data and run assigned AI tasks.
- Administrator: can manage settings,roles,and audit records.
The exact titles matter less than the boundaries. Roles should be reviewed when someone changes teams, takes on a new projector leaves the organization. Every permission should also have an owner: someone who can approve it, explain why it existsand remove it when it is no longer needed.
Keep Access Narrow
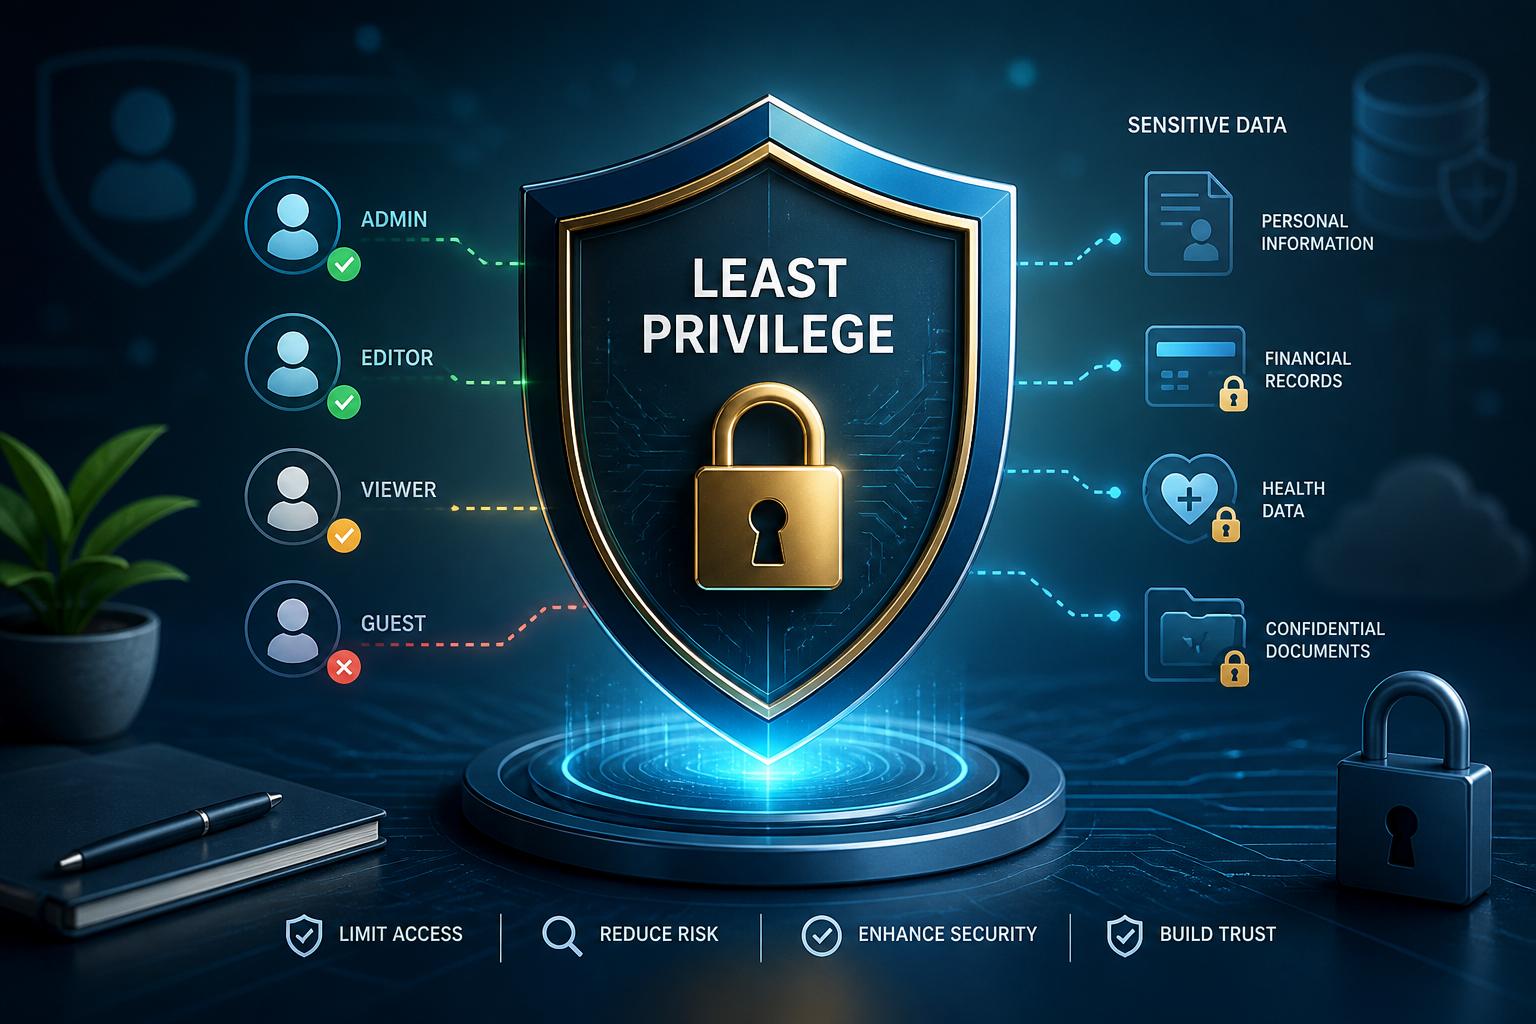
The principle of least privilege is simple: give people, service accountsand AI tools only the access required for the task at hand. Nothing more.
A support agent may need to view a customer’s account status, but not download the full customer database. A model that summarizes internal documents may need read-only access to a specific knowledge base, but no ability to change source files or retrieve payroll records. Keeping those boundaries tight limits the impact of mistakes, compromised credentials, and prompts that pull in information a user was never meant to see.
It also helps to separate different kinds of access. Viewing a record is not the same as editing it, exporting itor changing the settings that govern it.Export privileges,administrative controls,and access to sensitive prompts or proprietary files should be granted deliberately,not included by default.
Temporary access deserves the same care. Contractors, vendors, pilot programsand automated agents may need a permission for a limited period, but that permission should expire or be reviewed when the work ends.
Match Permissions to the Risk
Access to AI models should reflect the potential consequences of the work. A marketing writer may need a general-purpose writing tool with approved brand materials. A data analyst may need a model that can work with governed internal datasets. Neither role automatically needs permission to fine-tune a model, connect it to outside services, export sensitive promptsor trigger actions in other systems.
Set clear boundaries around wich models people can use, which data sources they can includeand what an output is allowed to do next. The more consequential the action, the more limited and visible the access should be.
This is especially important when an AI output could change a record, approve a transaction, deploy code, send a messageor publish content externally. A useful response from a model is not the same thing as authorization to act on it. For higher-risk actions, require human review before the result affects a customer, systemor business decision.
Access control in AI systems should cover the full path from prompt to outcome. It is indeed not enough to control who can open a model if that same person can use the output to make an unreviewed change in a sensitive system.
Review, Monitorand Adjust
Access decisions need a record. Teams should be able to see who requested access, which model or data source was involved, what policy allowed or denied the requestand whether a person approved a higher-risk action. Clear logs give security teams, auditorsand system owners something concrete to review when questions arise.
those records can also reveal problems over time: a role that keeps accumulating permissions, repeated attempts to access restricted informationor an automated agent operating outside its expected scope. Without visibility, it is difficult to know whether policies are working as intended.
access control is not a one-time setup task.People change jobs, contracts end, data becomes more sensitive, and AI tools gain new capabilities. Regular access reviews, time-limited permissions, alerts for unusual activityand prompt removal of unused privileges help keep access tied to a current and defensible business need.
The goal is not to make AI harder to use. It is indeed to make sure the right people can use the right tools and information for the right reasons-and that there is a clear answer when someone asks why they had that access in the first place.
AI tools built by Emerald Force
Built and supported by Emerald Force.
You might also like
- AI Can Build Websites: From HTML to Backend Scaffolds
- AI Voice Scams Are Rising: Why Verification Matters
- Letting AI Run Terminal Commands: Essential Safeguards
- AI Lowers Routine Costs, but Expertise Still Decides
- AI Agents Today: Useful but Still Need Oversight
- How AI Enables Robots to Perceive, Plan, and Interact
- Retrieval-Augmented Generation: A Clear Guide
- Why Smaller Tuned Models Win Focused AI Tasks
- Protect Family From AI Scams: Verify Before Paying
- Will AI Become Conscious? No Evidence So Far