
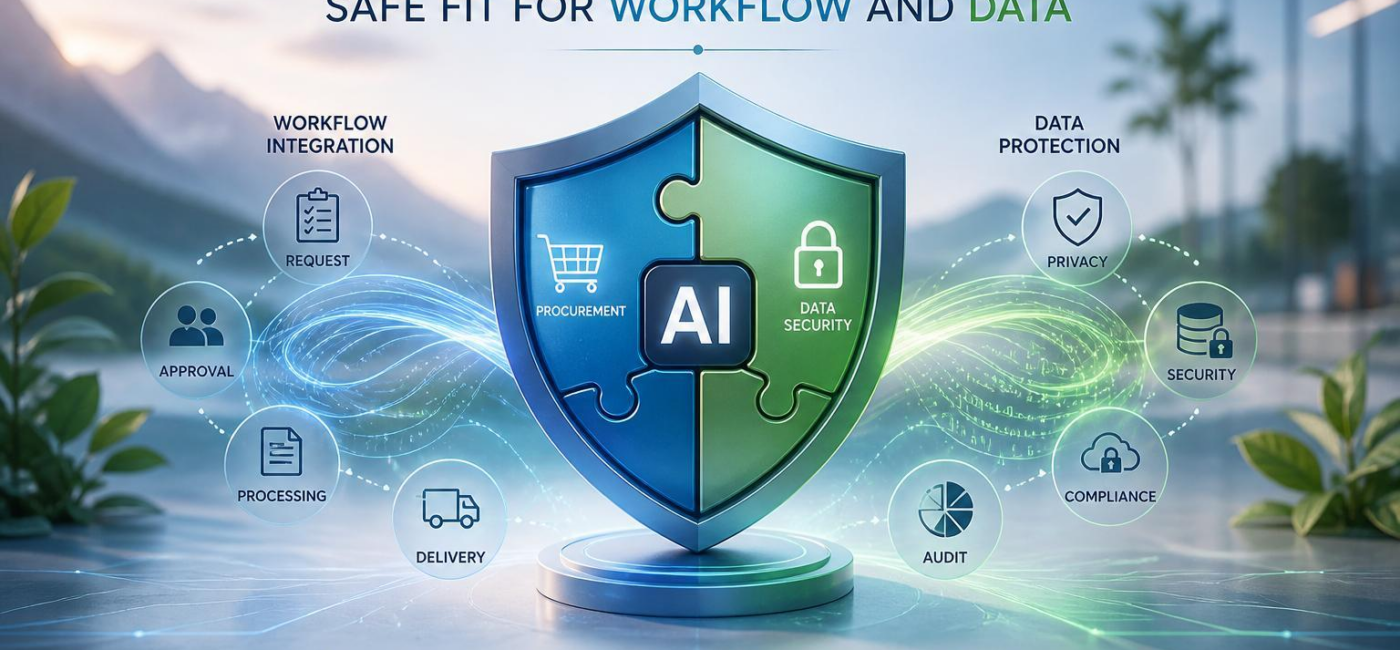
The most critically important AI procurement issue is simple: does the tool safely fit the way your association actually works and the data it handles? A long feature list means little if the system forces people into workarounds,creates unclear responsibilities,or exposes information that should remain protected. Start with the job to be done, then decide whether the AI tool can support it without weakening existing controls.
Start with the workflow
Before comparing vendors, map the proposed use case from start to finish.Look at the handoffs, approvals, exceptions, recordsand people involved. The question is not just whether the tool can produce a useful answer. It is whether employees can use it within the processes they already rely on.
A good fit works with existing identity management, document repositories, business applications, and escalation paths. It should be clear when someone is acting on an AI suggestion, how they can correct itand who is responsible if the output affects a customer, employee, supplieror regulated decision.If the tool creates a separate, informal process that nobody owns, it is likely to become a risk rather than a help.
Operational details matter early. Decide who will administer access, review usage, answer user questionsand coordinate with the vendor.Plan for training, testingand a workable way to pause or roll back the deployment if problems emerge. A pilot can often rely on closer manual review. A production system needs clearer ownership, dependable supportand controls that can hold up over time.
The safest purchase is not always the most sophisticated one.It is the one your organization can operate, superviseand stop responsibly.
Set clear rules for data
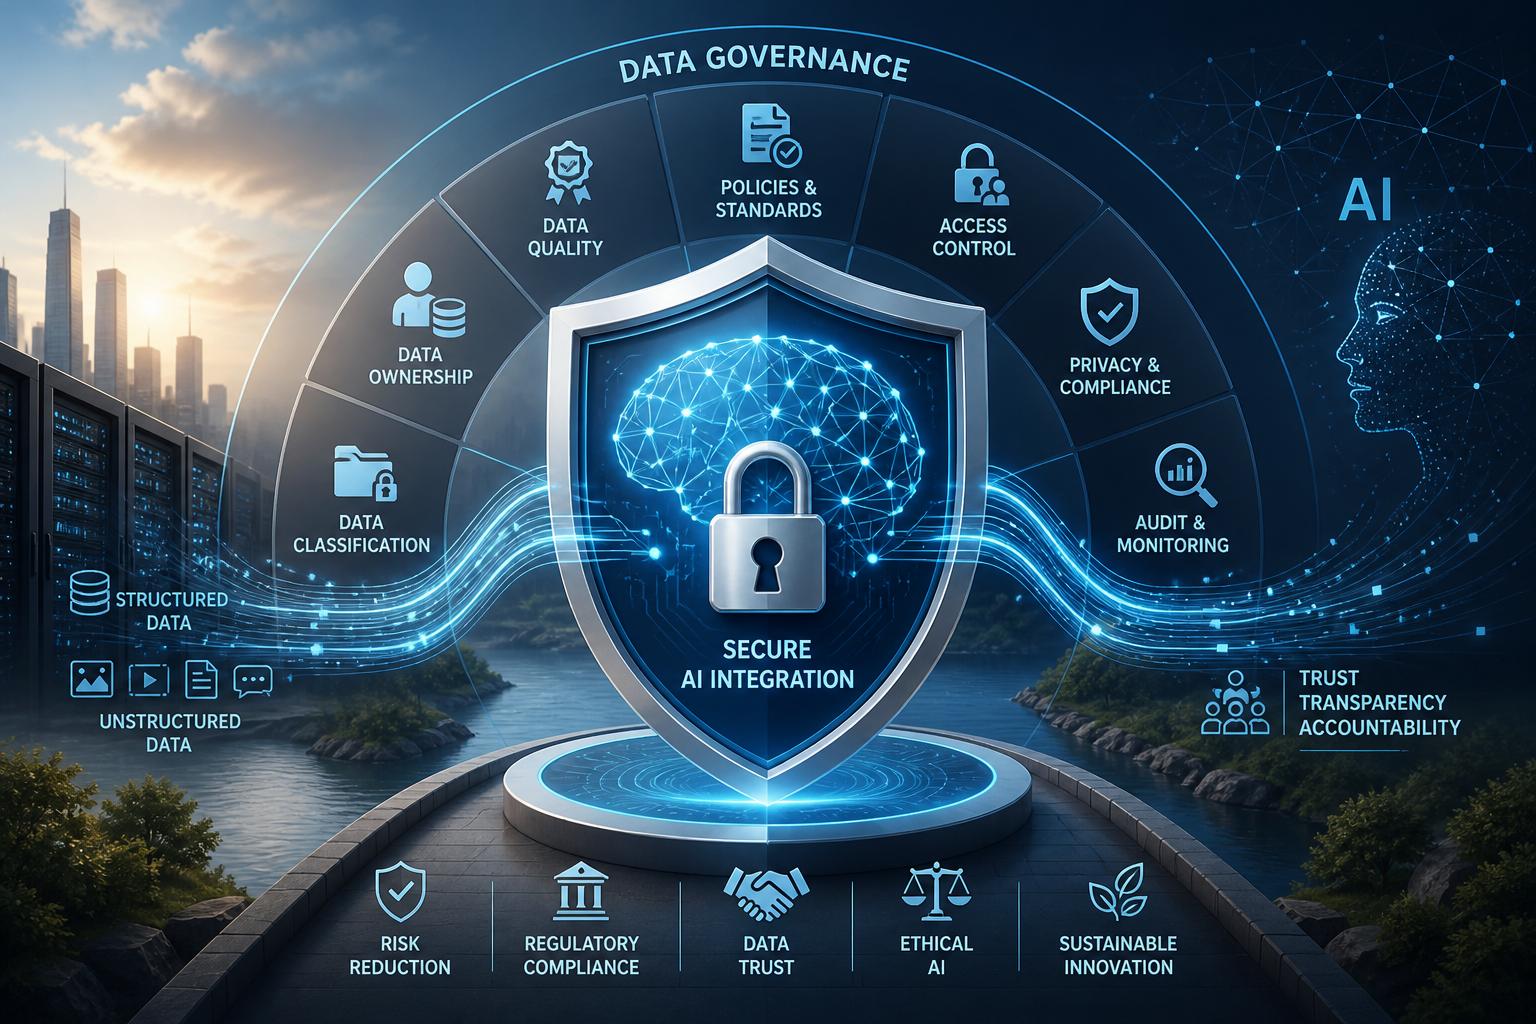
AI procurement also depends on knowing exactly what information the tool may access. Teams should distinguish between material that is appropriate for general assistance and information that needs tighter controls, such as customer records, employee files, financial details, source codeor regulated documents.
Each approved use case should have a named data owner. That person or team should be able to authorize access, set retention limitsand reconsider the arrangement as the workflow changes. Access should follow existing role-based permissions rather than creating informal exceptions for convenience.
Put the key requirements in writing: what data may be entered, what must never be entered, how long the provider keeps prompts and filesand whether customer content may be used for model training or service advancement. It should also be clear where processing takes place, which subprocessors are involved, how incidents are reportedand what happens to data when the contract ends.
An AI tool that is acceptable for drafting public-facing copy may not be appropriate for reviewing confidential contracts or analyzing personnel information. the right decision depends on whether the system’s permissions, logging, retention practicesand human oversight match the sensitivity of the work.
Review the vendor’s actual practices
A vendor review should focus on what the model will touch,what it may retain,and what decisions people may make based on its output. Ask direct questions about prompts,uploaded files,outputs,and usage data: Are they stored? Where are they processed? Who can access them? How long are they retained?
Contract language should reflect the answers,not broad assurances in a security statement. If the provider uses customer content for training, product improvementor another purpose, that should be stated plainly.The same is true for deletion procedures, data export, audit records, security incidents, and the vendor’s use of subcontractors.
the level of review should match the role the tool plays. A writing assistant used by trained staff presents different concerns from a system that ranks applicants, approves payments, or generates customer guidance. Higher-impact uses call for stronger testing, defined human review, clear escalation pathsand the ability to suspend use when the risk profile changes.
Keep control after launch
Signing the contract is only the beginning. once people start entering prompts, uploading filesand using generated output in their work, internal controls determine whether the tool remains appropriate. Assign named owners for security,privacy,legal review,workflow design,and day-to-day administration before access expands.
Begin with a limited deployment in a lower-risk workflow. Use approved data sources,a defined group of users,and clear expectations for reviewing results. Users need practical guidance, not just a policy document. They should know what information is prohibited, how to spot unreliable or unsupported outputand where to report suspicious behavior or possible data exposure.
For work that affects customers, employees, financial decisions, or regulated records, human review should remain part of the process. Keep useful audit records, maintain an incident-reporting path, and make sure administrators can quickly disable access if circumstances change.
Revisit the tool regularly. Features, integrations, vendor practicesand model behavior can change after purchase. Reviewing those changes, confirming that users are trainedand documenting approval before expanding use helps turn responsible AI procurement into an ongoing operating practice rather than a one-time checklist.
AI tools built by Emerald Force
Built and supported by Emerald Force.
You might also like
- Can AI Fake Photos? How Synthetic Images Look Real
- AI Handles Routine Service; Humans Handle the Rest
- How AI Can Scale and Tailor Misinformation
- AI Helps Both Sides: Security Choices Decide
- Few-Shot Prompting: Learning from a Few Examples
- Inference Cost: The Compute Behind Model Outputs
- How to Benchmark Tools Before Buying: A Practical Guide
- Can AI Remove Backgrounds? A Proven Vision Use Case
- How AI Clusters Customer Feedback and Detects Sentiment
- AI Center of Excellence: Standards and Adoption