
Can AI help defenders more than attackers? the honest answer is that it can help both. AI can make security teams faster adn more informed, but it can also make scams, reconnaissanceand social engineering easier to scale. The outcome depends less on the technology itself than on the security practices, incentivesand deployment choices around it.
How AI helps-and hurts-security
For defenders, AI can be useful when there is simply too much data for people to review quickly. It can help sort alerts, flag unusual activity, spot patterns in logs and messagesand give analysts more context before a small problem becomes a larger incident. Used well, it helps teams spend less time chasing routine noise and more time investigating what matters.
But the same strengths are available to attackers. AI can help them write more believable phishing emails, imitate a person’s tone, translate scams, research targetsand produce many variations of the same deceptive message. That does not turn every attacker into an expert, but it can make familiar attacks cheaper to produce and harder to dismiss at a glance.
The practical response is not panic. it is to reinforce the basics: verify unusual requests, protect accounts with strong identity controls, make reporting easyand give security teams the ability to investigate quickly. AI can support security judgment, but it cannot replace it.
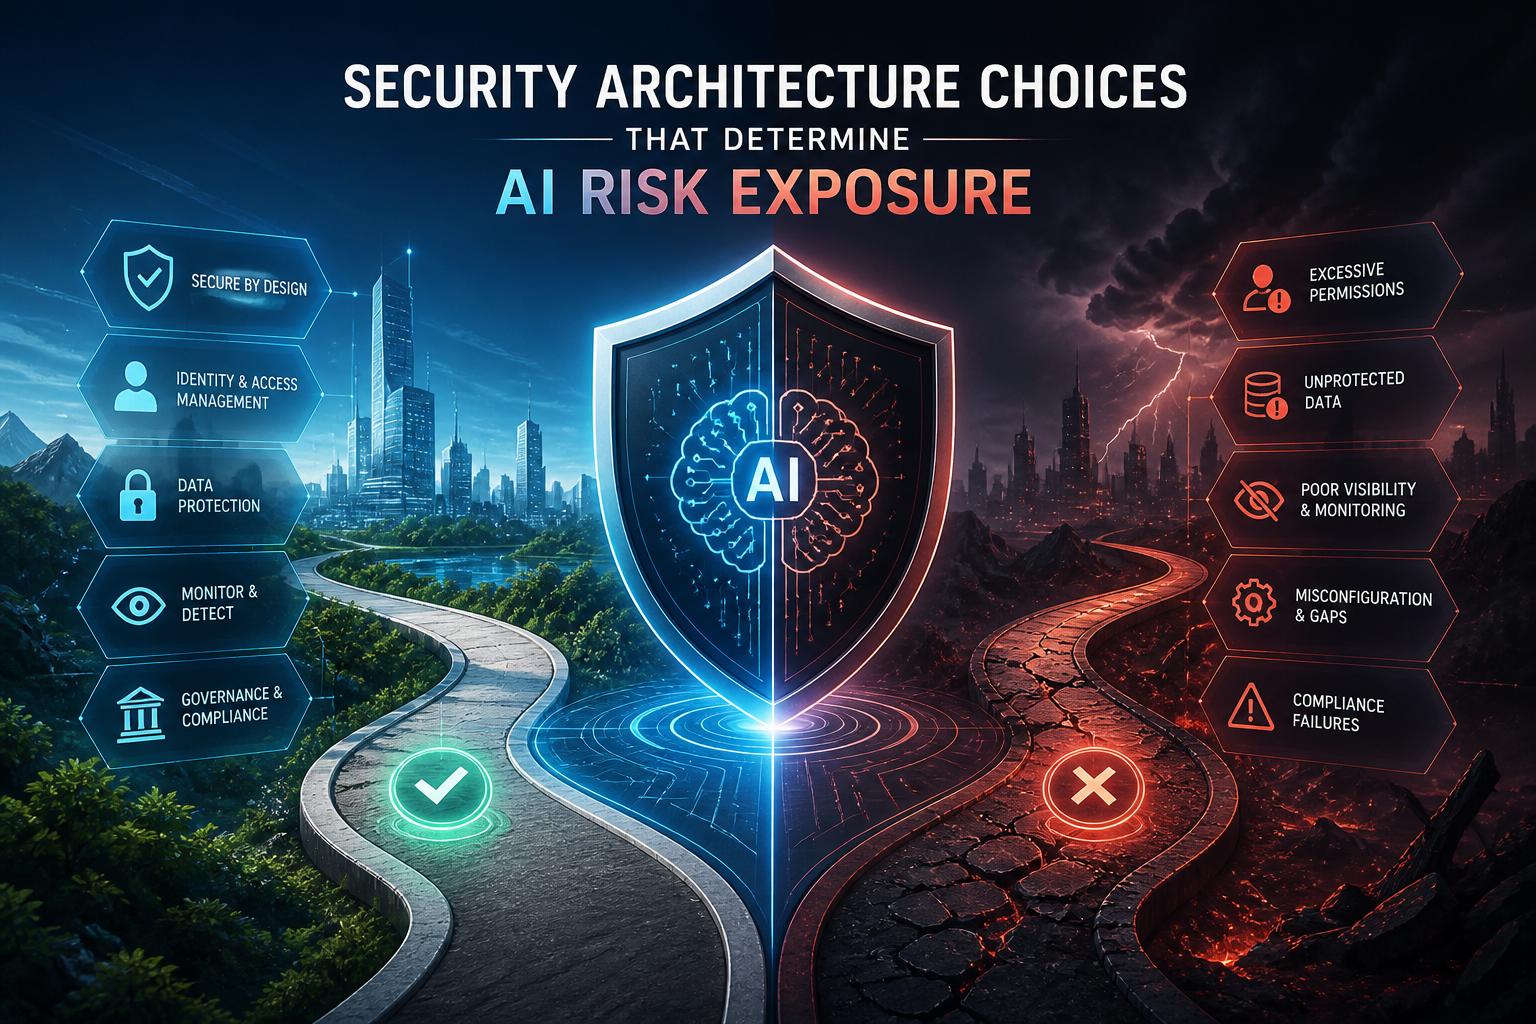
Design choices shape the risk
The risk of an AI system is not just about which model an organization chooses. It is about what sits around that model: who can use it, what data it can access, which tools it can calland what happens after it produces an answer.
A public-facing assistant connected directly to customer records, internal search, code repositoriesor administrative tools has a very different risk profile from one placed behind authenticated services with narrow permissions. The safer approach is to treat prompts as untrusted input and model output as something that still needs checks before it reaches a person, a systemor a customer.
This matters most when AI can take action. if a tool can send messages, change records, run codeor retrieve sensitive files, those actions should be limited and separately authorized. Sensitive information should not be dropped into prompts by defaultand access to internal material should respect the same permissions a user would have without AI.
Logs matter here, too. Teams should be able to review the request, the information retrieved, any tools usedand the final action taken. An isolated model may still give poor advice. A model connected to too many systems can turn a bad response,a manipulated prompt,or stolen credentials into a real operational problem. The useful question is simple: if someone manipulates this AI, how far can the effect spread?
Give someone obligation
AI projects need clear ownership from the start. Any system that handles sensitive information, influences security decisionsor acts for a user should have a business owner, a technical ownerand a clear path for escalation when something goes wrong. Governance is not bureaucracy for its own sake. It answers basic questions: who can approve changes, what data can be usedand when a person must make the final call.
The same discipline used for privileged accounts applies here. Keep permissions narrow, review access regularlyand require approval for changes that could have a serious impact. Set clear boundaries for the data an AI system may read, retainor send to outside services.If the system can change systems, release codeor contact customers, build in human approval before those actions occur.
Teams should also prepare for failure before it happens.Preserve useful logs, test how to pause or shut down the systemand make sure people know who is responsible for containment. Models can be misled by hostile prompts, poisoned data, incomplete contextor plain mistakes delivered with confidence. Testing should account for those possibilities before launch and whenever the model,its tools,or its data sources change.
Protect data and keep people in the loop
Good AI security starts with separating what a system may see, changeand recommend.Sensitive training data, prompts, model assets, and decision records should not all be broadly available in one place. Assign an owner to each dataset, limit access to the people and systems that need itand revisit those permissions as employees, vendorsand projects change.
The familiar safeguards still apply: encryption, secure backups, audit logsand tested incident-response procedures. Data should also be checked before it enters an AI workflow. Outdated, poorly sourcedor deliberately manipulated information can distort results long before anyone sees an obvious warning sign.
Human judgment deserves the same protection. A confident answer is not proof, especially when a proposal affects money, safety, employment, health care, or individual rights.Give reviewers enough context to challenge a result, including the source material, known limitsand uncertainty behind the recommendation.Keep a person accountable for consequential decisions, document meaningful overridesand retain records so mistakes can be examined and corrected.
AI will not decide the outcome on its own
Can AI help defenders more than attackers? It can-but only when organizations make careful choices about access, data, oversightand accountability. Attackers will use AI to make old tactics faster and more convincing. Defenders can use it to spot threats sooner and reduce the burden on their teams.
The difference comes down to preparation. Organizations that limit access, verify high-impact actions, test their systemsand keep people responsible for final decisions will be in a stronger position to benefit from AI without handing attackers an easier path in.
AI tools built by Emerald Force
Built and supported by Emerald Force.
You might also like
- AI Handles Routine Service; Humans Handle the Rest
- How AI Can Scale and Tailor Misinformation
- AI Helps Both Sides: Security Choices Decide
- Few-Shot Prompting: Learning from a Few Examples
- Inference Cost: The Compute Behind Model Outputs
- How to Benchmark Tools Before Buying: A Practical Guide
- Can AI Remove Backgrounds? A Proven Vision Use Case
- How AI Clusters Customer Feedback and Detects Sentiment
- AI Center of Excellence: Standards and Adoption
- Where AI Coding Excels: Tests, Refactors, Scaffolds